Authorization disclaimer. This walkthrough is limited to the intentionally vulnerable PortSwigger Web Security Academy lab linked below. Test only systems you own or are explicitly authorized to assess.
Overview
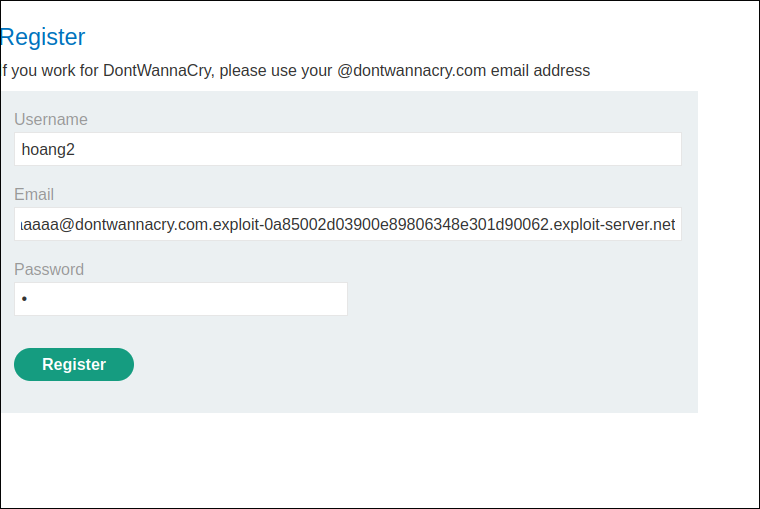
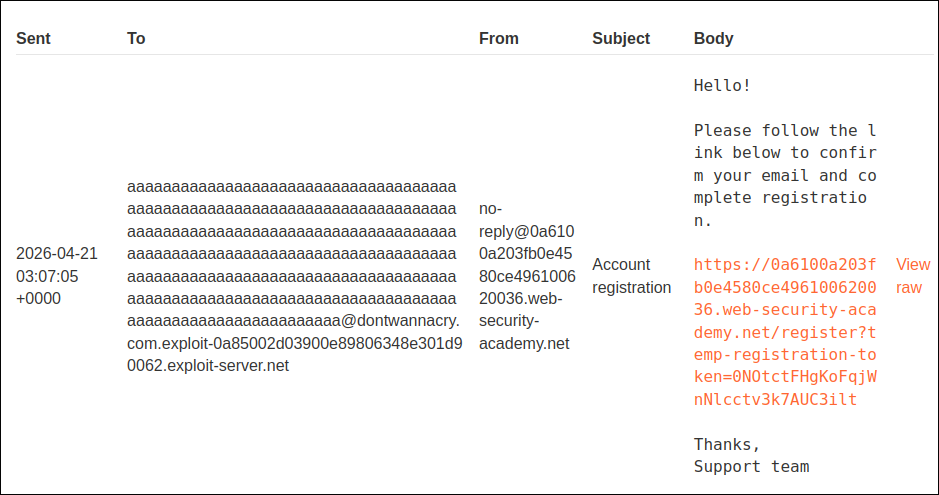
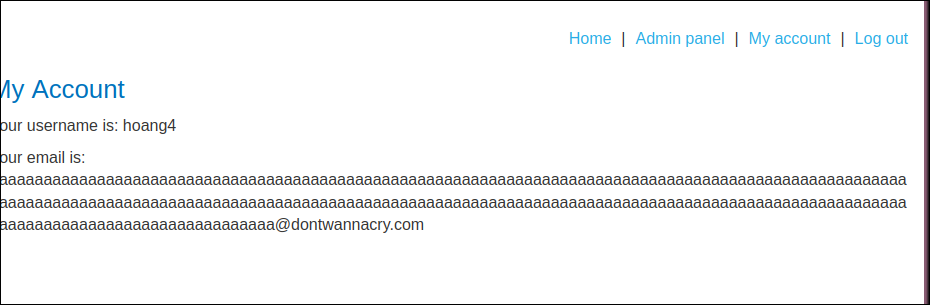
An overlong registration value is handled differently by separate components, creating an account identity that later satisfies a privileged-domain check.
Lab objective/setup
This intentionally vulnerable Academy exercise isolates inconsistent handling of exceptional input. The supplied accounts and endpoints are used to reproduce only the source note evidence for inconsistent handling of exceptional input; all request changes remain inside this Academy instance.
What I observed
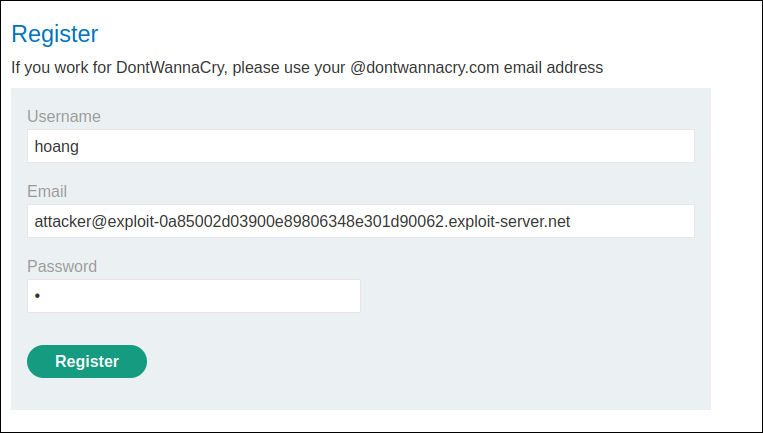
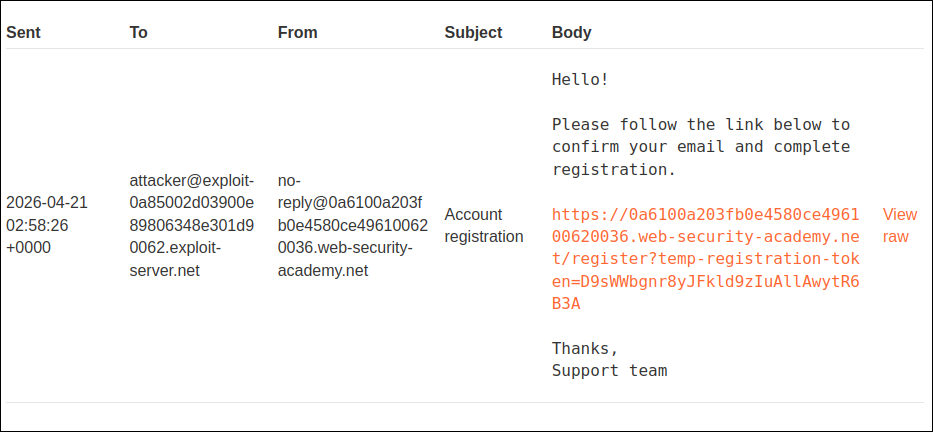
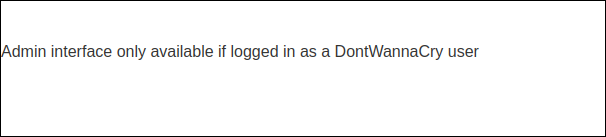
The baseline capture for inconsistent handling of exceptional input establishes the intended request and response before any mutation. Subsequent replays isolate the input or state transition responsible for inconsistent handling of exceptional input, and the response evidence shows exactly when the lab accepts the unintended behavior.
Why it is vulnerable
Inconsistent length handling and normalization across workflow stages can transform rejected input into a security-relevant value.
Walkthrough in the authorized PortSwigger lab
- Capture the baseline request for inconsistent handling of exceptional input and record the response that represents the intended lab workflow.
- Replay the recorded mutation that exposes inconsistent handling of exceptional input, keeping the session and other fields unchanged.
- Confirm the inconsistent handling of exceptional input signal in the response before applying the next source-documented operation.
- Complete the Academy objective using only the confirmed inconsistent handling of exceptional input behavior and the supplied synthetic account or product data.
1 | <overlong-local-part>@dontwannacry.com.<lab-exploit-server> |
Verification
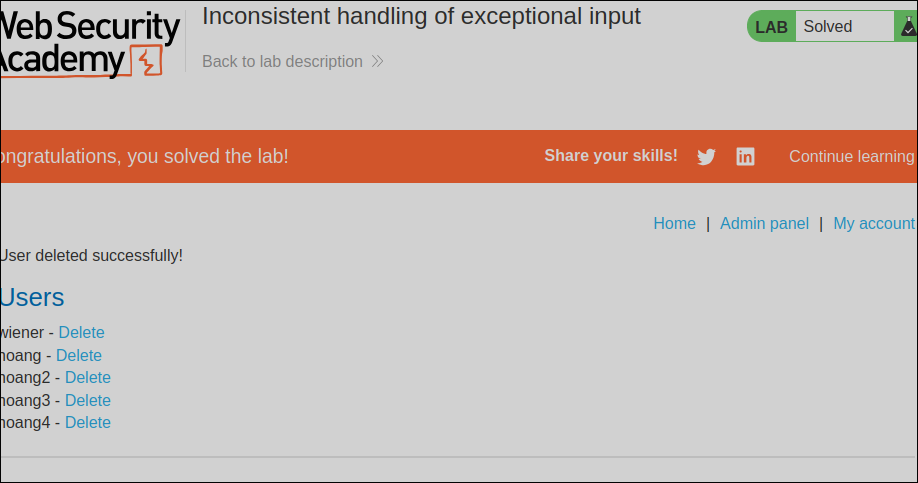
The final capture shows the Academy marking the inconsistent handling of exceptional input exercise as solved after the documented request sequence. No testing was performed outside the isolated lab.
Impact and defensive lesson
The evidence demonstrates the concrete risk of inconsistent handling of exceptional input: a server-side trust decision can be bypassed through the exact input or workflow shown in this lab. For inconsistent handling of exceptional input, the server must enforce the exact invariant violated in the captured sequence and regression-test that mutation alongside the normal path.