Authorization disclaimer. This walkthrough is exclusively for the intentionally vulnerable PortSwigger Web Security Academy lab linked below. Only test systems you own or are explicitly authorized to assess.
Overview
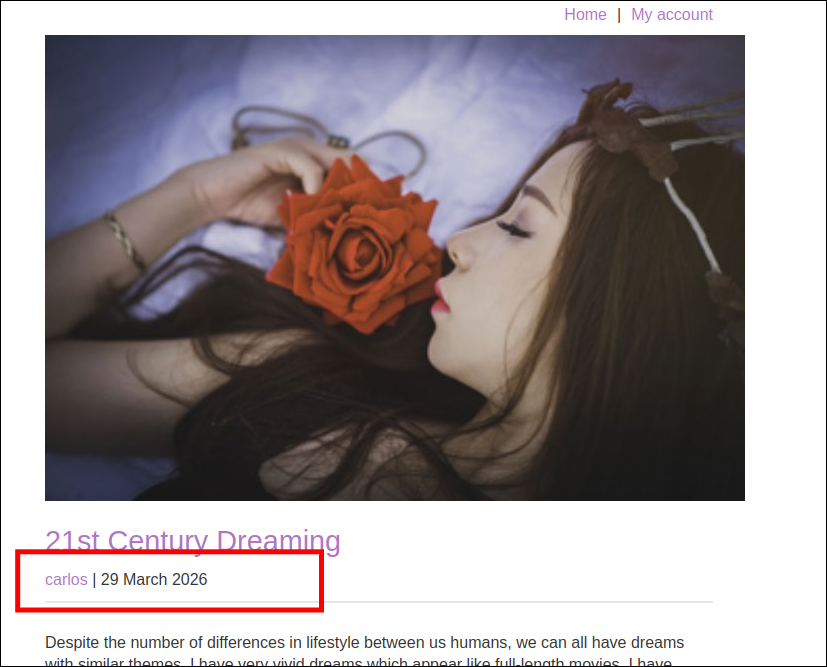
The account endpoint uses GUID-like identifiers rather than predictable usernames or integers. That makes guessing harder, but the application publishes Carlos’s identifier in an author link. Once discovered, the GUID can be supplied to the unprotected account endpoint to retrieve his synthetic API key.
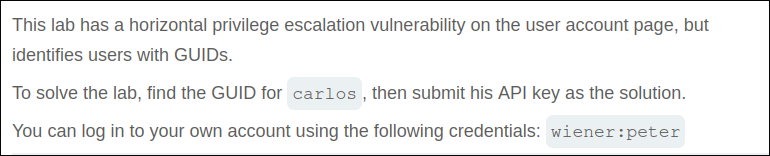
Lab objective/setup
Sign in as wiener:peter, discover Carlos’s user identifier, access his account record, and submit the synthetic API key.
What I observed
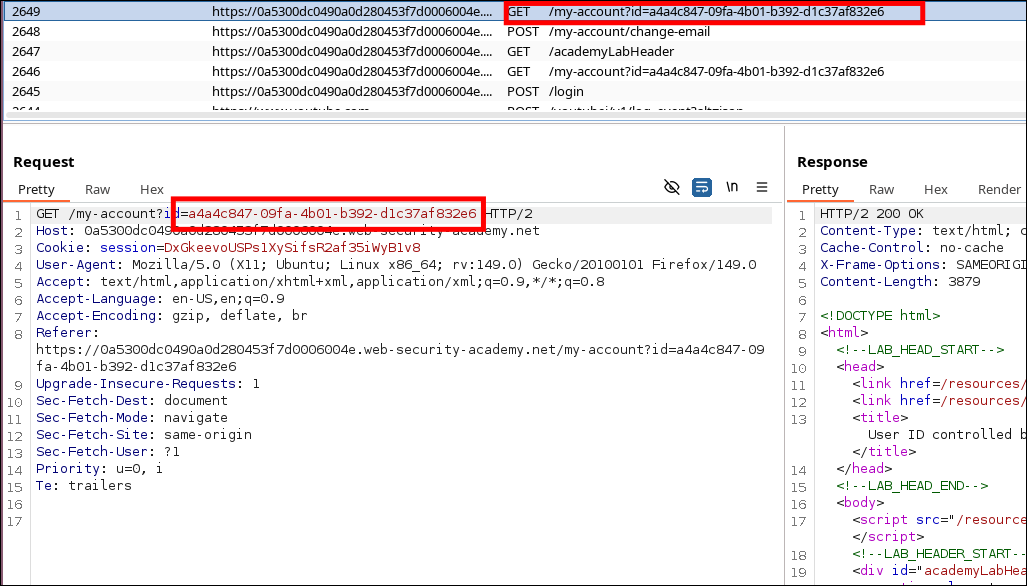
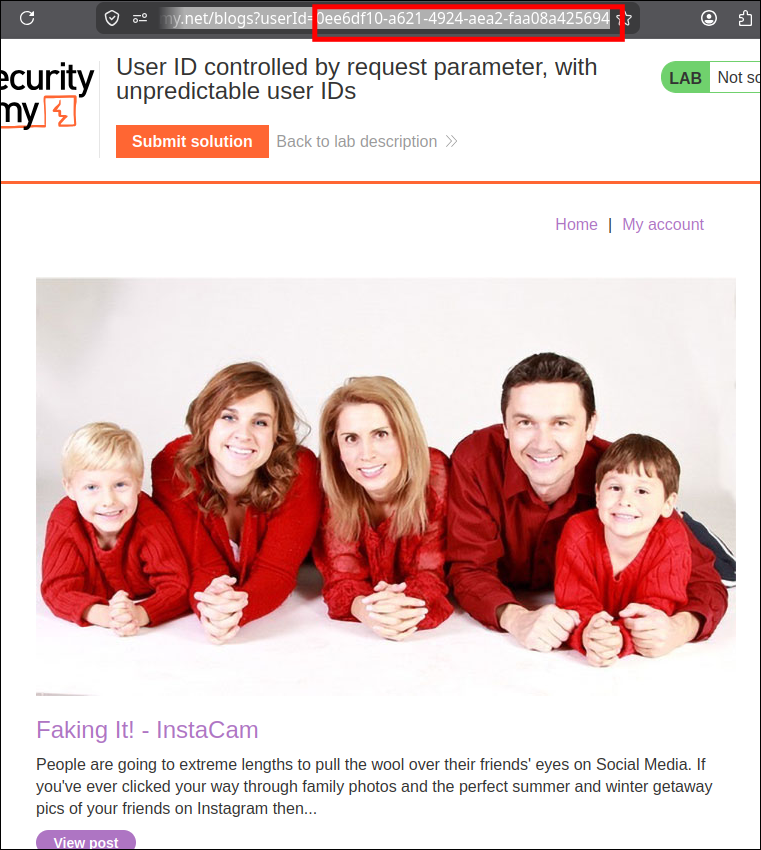
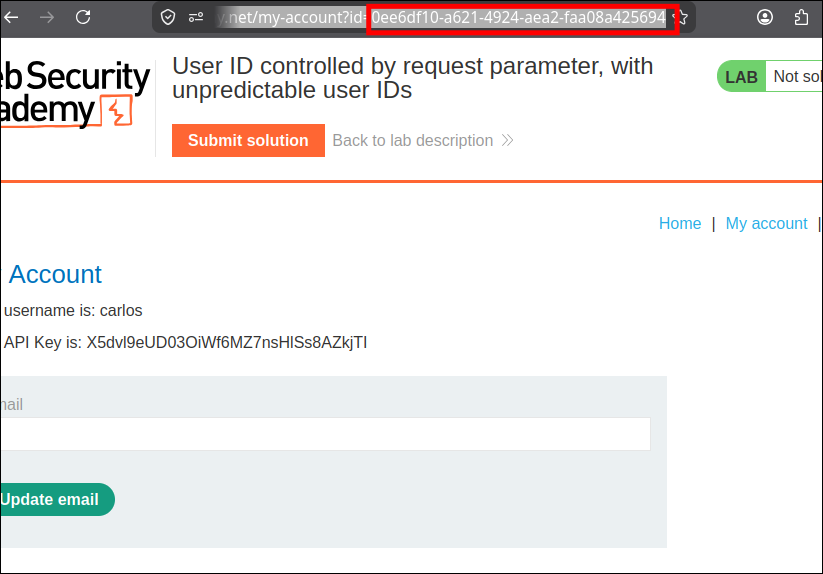
The authenticated account URL contained a long identifier, preventing simple enumeration. Elsewhere on the site, blog posts linked authors through /blogs?userId=<GUID>. Finding a post by Carlos therefore disclosed the exact identifier needed by /my-account?id=<GUID>.
Why it is vulnerable
Identifiers answer which object is requested, not whether the requester may access it. GUID entropy can reduce blind guessing but cannot survive disclosure through links, logs, analytics, or other application features. The account handler must compare the requested object with the authenticated principal’s permissions.
Walkthrough in the authorized PortSwigger lab
- Log in as
wienerand note the GUID-based account URL. - Browse the blog and locate a post authored by
carlos. - Copy Carlos’s GUID from the author link.
- Supply it as the
idvalue on/my-accountand retrieve the synthetic API key. - Submit the key through the lab interface.
Verification
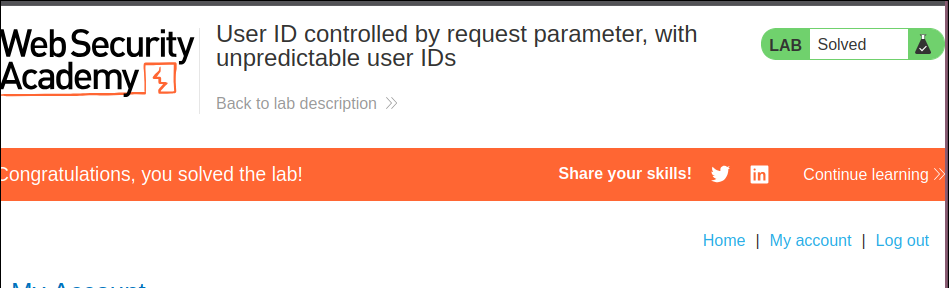
Carlos’s identifier is obtained from a public blog relationship rather than guessed. Using that value on the account endpoint returns his protected data, and the Academy accepts the exposed key.
Impact and defensive lesson
Real-world variants expose personal records, invoices, tokens, or tenant data whenever an identifier leaks. Treat opaque IDs as defense in depth only; enforce object-level authorization for every read and write, regardless of identifier format.