Authorization disclaimer. This walkthrough is exclusively for the intentionally vulnerable PortSwigger Web Security Academy lab linked below. Only test systems you own or are explicitly authorized to assess.
Overview
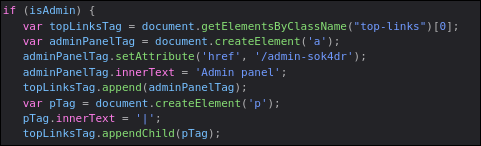
The application replaces a familiar admin path with a randomized one, but does not protect it with server-side authorization. Public JavaScript contains the route, so any visitor can recover it.
Lab objective/setup
With no credentials, find the panel and delete the synthetic carlos account.
What I observed
robots.txt did not provide a useful path. Inspecting the page’s client-side source instead revealed /admin-sok4dr embedded in JavaScript.
Why it is vulnerable
Everything delivered to a browser is observable by the user. A secret URL cannot establish identity or privilege, and this route has no independent authorization gate.
Walkthrough in the authorized PortSwigger lab
- Inspect the home page source or loaded JavaScript.
- Identify
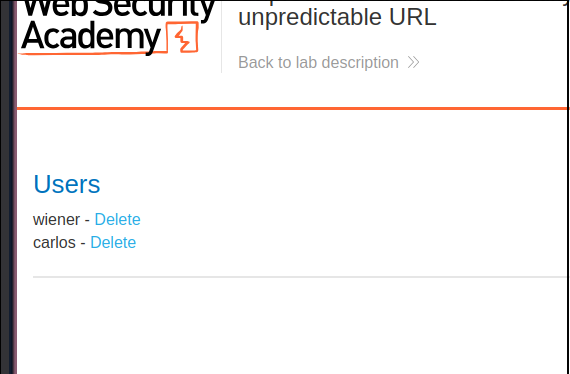
/admin-sok4dr, request it directly, and confirm the panel is accessible. - Delete
carlosusing the provided control.
Verification
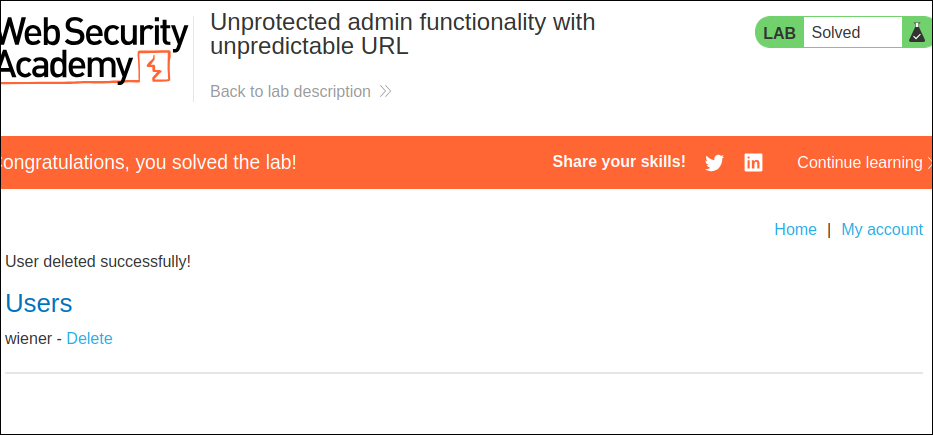
The solved banner confirms the action. Reaching the panel in a fresh unauthenticated session demonstrates that possession of the URL is the only control.
Impact and defensive lesson
Obscure routes may reduce accidental discovery, but they provide no authorization. Require a validated session and appropriate server-side role on every admin endpoint.